WINDOWS / SHAREPOINT / MICROSOFT ENTRA
365CANOPY
FOCUSSHAREPOINT ACCESS
COLLECTORREAD OPERATIONS
BUILDPUBLIC ALPHA
Follow the branches of access. Trace SharePoint library permissions through folders and groups to the people they reach.
A permission is more useful when you can follow it all the way to a person.
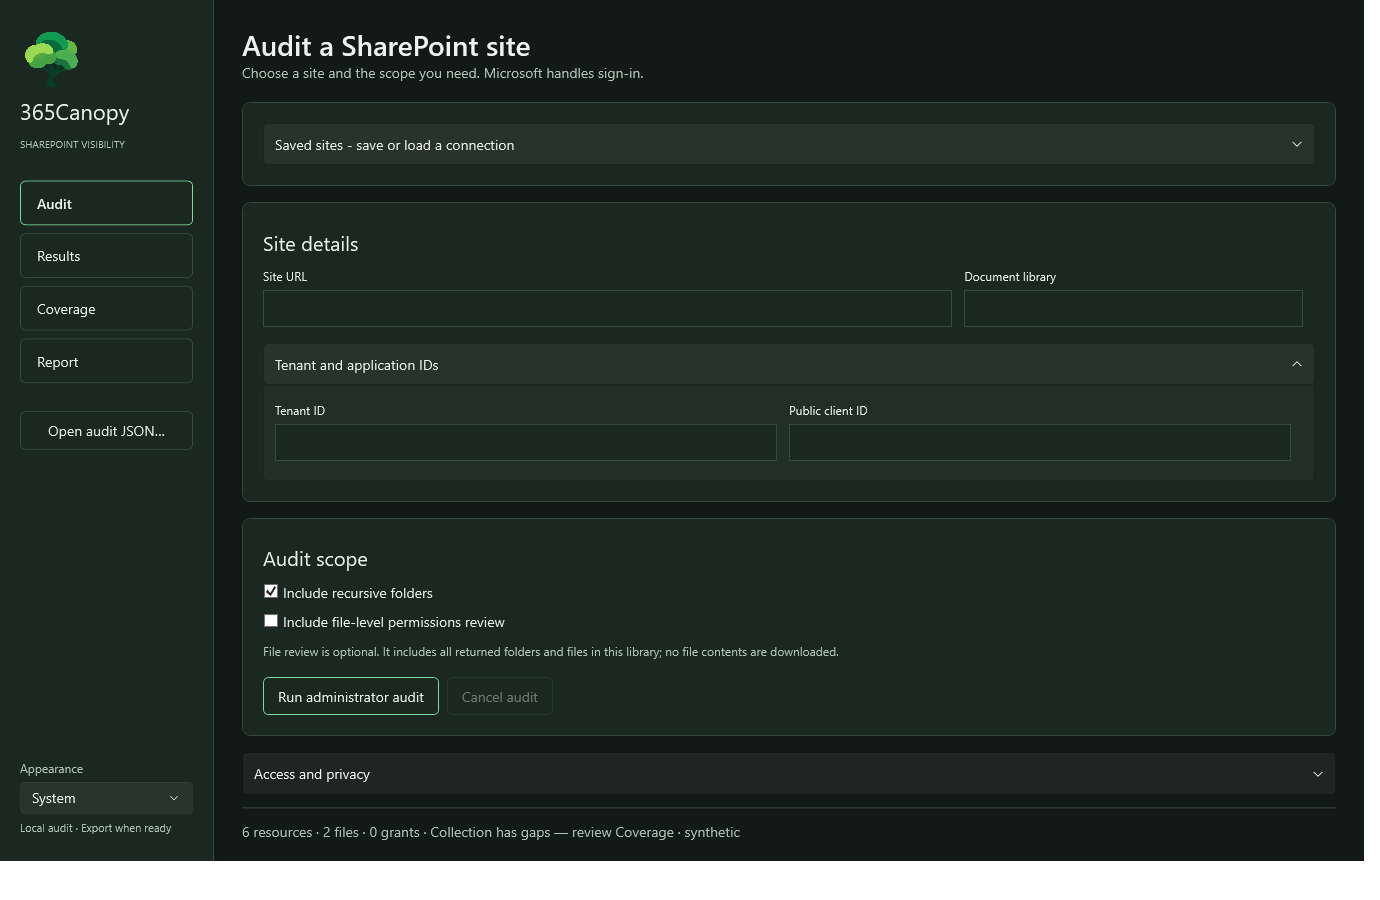
PUBLIC RECORD / CURRENT SCOPE
365Canopy is an open-source Windows desktop permissions audit tool for SharePoint document libraries. Explore permission inheritance, unique grants, classic SharePoint groups, and Microsoft Entra membership in one reviewable record.
Start with a site and document library, inventory its folders, and optionally include file-level permissions. Canopy traces observed grants through SharePoint and Entra groups, including available members, owners, and usernames. Separate Audit, Results, Coverage, and Report views keep the collection and its limits legible.
Export an offline HTML permissions tree with expandable groups and people, or use CSV and JSON for further review. Audit evidence stays in application memory until explicit export. Named connection profiles are saved only on request and protected for the current Windows account; they contain connection settings, not credentials or audit results.
The public alpha is available with a Windows x64 setup executable and matching SHA-256 file on GitHub Releases. The installer includes .NET and PowerShell; the one-time audit dependency setup downloads PnP.PowerShell after review of upstream terms and verifies its archive hash. Setup requires an organization-owned single-tenant public-client registration and administrator consent. The collector uses read operations, but tested SharePoint consent includes write-capable AllSites.FullControl. It does not create registrations or grant consent during an audit.
This is observed permission evidence, not a complete effective-access evaluator. File contents, versions, sharing-link details, and policy-aware access decisions are outside the preview. Hidden membership, inaccessible resources, API omissions, and a 40,000-item file-discovery limit can leave gaps. A missing person or grant does not establish absence of access.
DESIGN DIRECTIVES
WHAT THE SYSTEM
REFUSES TO FORGET.
FOLLOW THE GRANT
Connect permission sources, inherited access, groups, and observed people.
KEEP GAPS VISIBLE
Partial collection remains partial; unknown access never becomes a clean bill of health.
CARRY THE EVIDENCE
Export a navigable permissions tree and structured records while keeping tenant identities private.
OPERATING SEQUENCE / WINDOWS INSTALLER / AVAILABLE NOW
- 01SET LIBRARY SCOPE
- 02TRACE PERMISSIONS
- 03REVIEW COVERAGE
- 04EXPORT THE TREE